NetTcpBinding 以 TCP 為傳輸層,安全模式分三類:
測試環境:服務端 Win2008 (VS2008, .NET 3.5, IIS 7.0),客戶端同機與 Win2003 另一台。採自宿主 Console、程式碼配置。
[ServiceContract(Namespace = "https://chnking.com")]
public interface IGetIdentity
{
    [OperationContract]
    string Get(string ClientIdentity);
}
public class GetIdentity : IGetIdentity
{
    public string Get(string ClientIdentity)
    {
        return "服務端Identity是'" + ServiceSecurityContext.Current.PrimaryIdentity.Name +
               "'\r\n客戶端Identity是 '" + ClientIdentity + "'";
    }
}
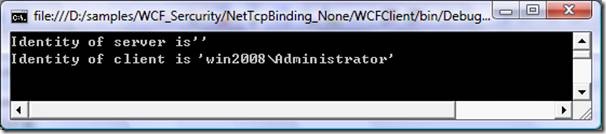
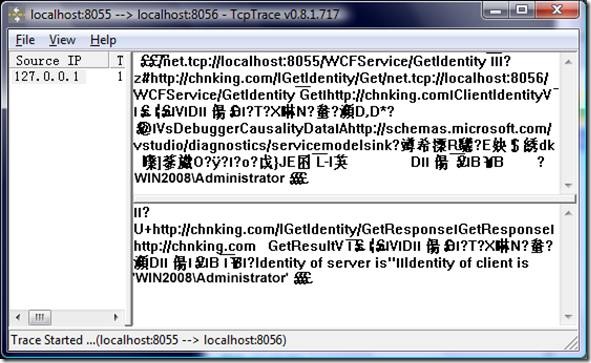
無加密、無驗證,Binary 編碼明文可見。適合受信任內網效能測試。
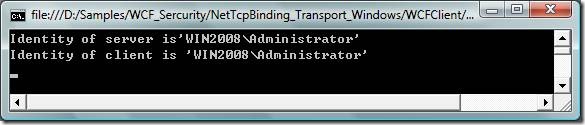
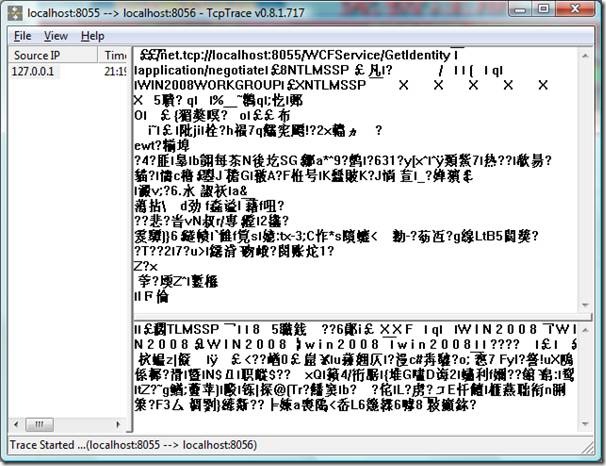
Windows Security 直接保護 TCP 連線,提供完整性、機密性、雙向驗證。程式碼僅需設定 SecurityMode.Transport 與 TcpClientCredentialType.Windows。封包經加密,Binary 內容不可讀。
需服務端憑證建立 TLS 通道,客戶端匿名。產生憑證:makecert -sr localmachine -ss My -n CN=win2008 -sky exchange -pe -r。服務端與客戶端皆設定 TcpClientCredentialType.None 並指定服務端憑證;客戶端略過憑證驗證。
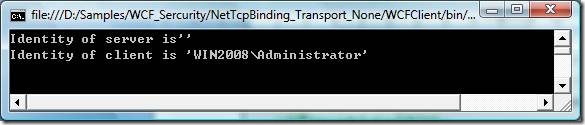
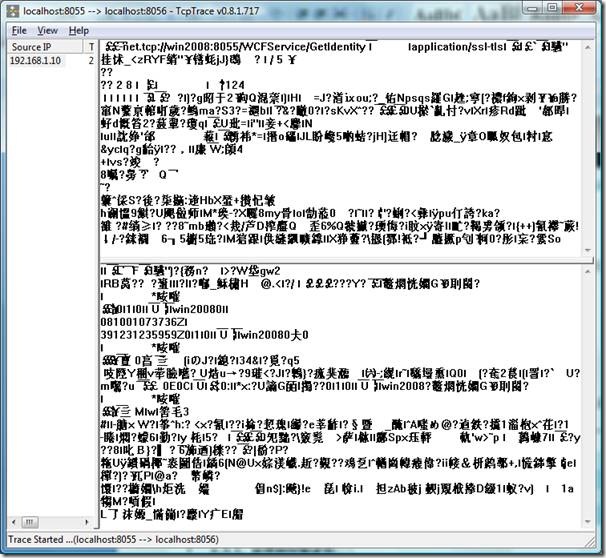
服務端憑證建立 TLS,客戶端憑證互相驗證。雙方各需憑證:伺服器 CN=win2008,客戶端 CN=TestClient。服務端關閉客戶端憑證驗證模式;客戶端指定自身憑證並略過伺服器驗證。
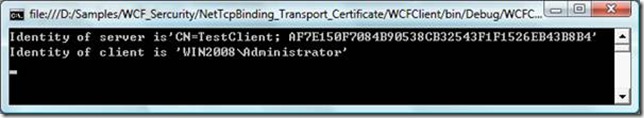
同 Message 模式,啟用 MapClientCertificateToWindowsAccount 後,需在 AD 環境配置映射: