蠕蟲自動化利用 IIS 漏洞 (CodeRed, Nimda) 後,攻擊焦點轉向資料庫層。ASP/PHP/JSP 動態網站若忽略資料庫安全,等同大門加鎖卻留後門大開。
Function Filter_SQL(strData)
    Dim strFilter, blnFlag, i, arrayFilter
    strFilter = "',;,//,--,@,_,exec,declare"  ' 可擴充
    blnFlag = False
    arrayFilter = Split(strFilter, ",")

    For i = 0 To UBound(arrayFilter)
        If InStr(strData, arrayFilter(i)) > 0 Then
            blnFlag = True
            Exit For
        End If
    Next

    If blnFlag Then
        Response.Redirect "wrong.asp"  ' 記錄攻擊來源、IP、時間
    Else
        Filter_SQL = strData
    End If
End Function
SELECT/INSERT/UPDATE/DELETE,無 DROP/ALTER/xp_*-- 語法
EXEC xp_cmdshell 'command_string' [, no_output]
-- 實際攻擊鏈
EXEC xp_cmdshell 'net user hacker P@ssw0rd /add'; -- 建立系統用戶
EXEC xp_cmdshell 'net localgroup administrators hacker /add'; -- 提權至管理員
| 版本 | 預設權限 | 代理帳戶機制 |
|---|---|---|
| SQL 2000 | sysadmin 固定角色 | xp_sqlagent_proxy_account → SQLAgentCmdExec |
| SQL 2005+ | sysadmin + 授權者 | ##xp_cmdshell_proxy_account## 憑證 |
| 預存程序 | 風險 | 建議 |
|---|---|---|
| xp_cmdshell | OS 命令執行 | 嚴格管控/停用 |
| xp_regread/xp_regwrite | 登錄讀寫 | 移除 PUBLIC 執行權 |
| xp_fileexist/xp_dirtree | 檔案系統列舉 | 移除 PUBLIC 執行權 |
| sp_OA* | OLE Automation 物件建立 | 停用 Ole Automation Procedures |
| xp_sendmail | 郵件發送/資料外洩 | 遷移 Database Mail |
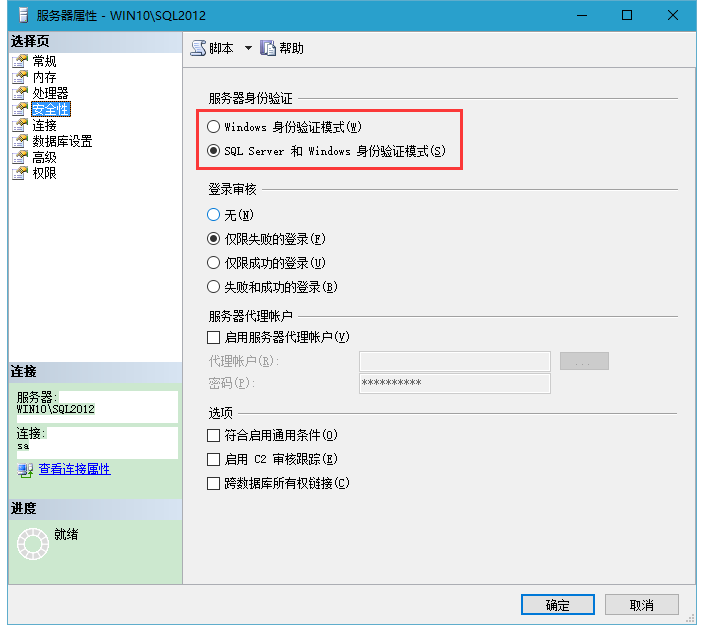
資料庫安全不是單一設定,而是分層防禦體系。sa 空密碼與 xp_cmdshell 開放是「必死」配置,修復這兩點即消除 80% 以上自動化攻擊向量。