使用 NetTcpBinding、Message 安全模式與 UserName 認證進行自我宿主時,啟動 ServiceHost 即拋出:
The ChannelDispatcher at 'net.tcp://localhost:9001/WCFService' with contract(s) '"IWCFService"' is unable to open its IChannelListener.
移除配置文件中的 <security mode="Message"> 區塊後錯誤消失。
WCF 規定:Message 安全模式強制要求服務端提供 X.509 憑證,用於加密 SOAP 訊息標頭與主體。配置文件中雖指定了 clientCredentialType="UserName",但缺少 <serviceCertificate> 設定,導致通道建構階段驗證失敗,無法開啟監聽器。
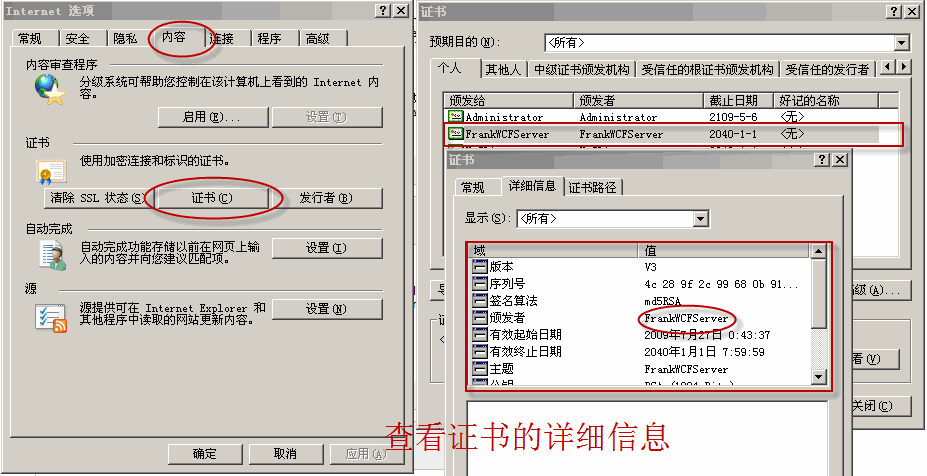
makecert -r -pe -n "CN=FrankWCFServer" -ss My -sky exchange憑證將存放於「目前使用者 → 個人」存儲區。
<serviceBehaviors>
  <behavior name="WCFService.WCFServiceBehavior">
    <serviceMetadata httpGetEnabled="true" />
    <serviceDebug includeExceptionDetailInFaults="false" />
    <serviceCredentials>
      <serviceCertificate x509FindType="FindBySubjectName" findValue="FrankWCFServer" storeLocation="CurrentUser"/>
      <clientCertificate>
        <authentication certificateValidationMode="None"/>
      </clientCertificate>
      <userNameAuthentication userNamePasswordValidationMode="Custom" customUserNamePasswordValidatorType="WCFService.MyUserNamePasswordValidator,WCFService"/>
    </serviceCredentials>
  </behavior>
</serviceBehaviors><wsHttpBinding>
<binding name="MessageAndUserName">
<security mode="Message">
<message clientCredentialType="UserName"/>
</security>
</binding>
</wsHttpBinding>加入服務憑證配置後,ServiceHost.Open() 成功,客戶端可正常呼叫驗證邏輯。
certificateValidationMode="None" 以簡化信任鏈驗證,專注於業務邏輯驗證。