本文詳細闡述 ASP.NET 2.0 中 IIS 整合 Windows 驗證與 ASP.NET Windows 驗證的運作機制,涵蓋 NTLM/Kerberos、WindowsAuthenticationModule、IPrincipal/IIdentity 建構全流程。
HttpContext.WorkerRequest。WindowsAuthenticationModule(在 <authentication mode="Windows"/> 時啟用)於 AuthenticateRequest 事件中取出權杖。WindowsIdentity → WindowsPrincipal(含角色列表,透過 P/Invoke 取得 Windows 群組)。WindowsPrincipal 存入 HttpContext.User,供後續授權模組使用。Thread.CurrentPrincipal 同步設為 HttpContext.User。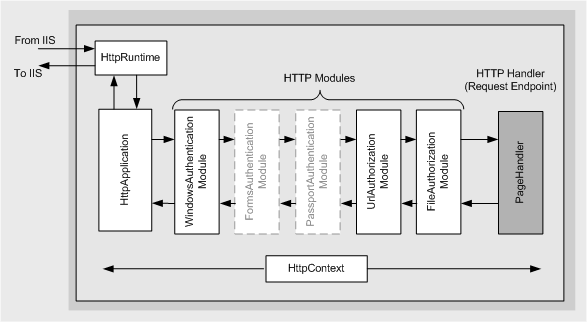
請求經過 HttpApplication → 多個 HTTP 模組(含驗證模組) → HTTP 處理常式。HttpContext 貫穿生命週期傳遞請求/回應資訊。
<authentication mode="Windows" />
<!-- machine.config/web.config 中預設已註冊 WindowsAuthenticationModule -->
無需撰寫任何驗證代碼,即可在頁面透過 User.Identity.Name 取得 DOMAIN\username。